Safer Internet Day: India’s Data Protection Law Journey (2000–2027)
India's data protection law from the IT Act 2000 and 2017 privacy ruling to the DPDP Act 2023, 2025 Rules and phased dates to May 2027: what's in force.
Latest Story
Every time you install an app, pay by UPI or ask an AI assistant a question, someone collects data about you. For most of the internet era, India had no dedicated law saying what they could do with it. This page traces the India data protection law timeline from the Information Technology Act of 2000, through the 2017 judgment that made privacy a fundamental right and two failed bills, to the Digital Personal Data Protection (DPDP) Act, 2023 and the Rules notified in November 2025. It also shows what is actually in force today, what is still only scheduled, and what you can do in the meantime.
💡 Short Answer
India’s data protection law is the Digital Personal Data Protection Act, 2023, which received assent on 11 August 2023. Its Rules were notified on 13 November 2025 with a phased start: the Data Protection Board and definitions immediately, Consent Managers on 13 November 2026, and most duties and rights on 13 May 2027. Before it, India relied on the IT Act of 2000, its 2008 amendments and the 2011 SPDI Rules.
India’s Data Protection Law: Key Questions
India’s Privacy Law in Ten Points
- 2000: the IT Act was a cyber and e-commerce law, not a privacy law.
- 2009–2011: Sections 43A and 72A and the SPDI Rules gave the first, narrow data duties.
- 2017: Puttaswamy made privacy a fundamental right, 9–0.
- 2018: the Srikrishna Committee drafted a full data protection bill.
- 2019–2022: the PDP Bill went to a JPC and was withdrawn.
- 2023: the DPDP Act passed in a week; assent on 11 August.
- 2025: Rules notified on 13 November; an 18-month phased start began.
- Today: the Board exists on paper; its members are not yet appointed.
- Next: Consent Managers on 13 November 2026, the main phase on 13 May 2027.
- The test: whether people can actually use their rights and get a complaint heard.
What Is Actually in Force on 9 October 2026
Enactment, notification and commencement are three different things. This is where each part stands.
The most common mistake in coverage of the DPDP Act is to treat the date it was passed, or the date its Rules were published, as the date it started protecting people. In fact the commencement notification of 13 November 2025 split the Act into three groups. The first group, in force now, mostly builds the machinery: definitions, the Data Protection Board, the penalty schedule and the government’s rule-making powers. It also brought one controversial change into force at once: the amendment to the Right to Information Act that widens the exemption for personal information.
The provisions that change what an app or a bank must do with your data, and what you can demand of it, are in the third group. Until 13 May 2027, the older IT Act regime continues to apply.
| Piece of the framework | Status on 9 Oct 2026 | Date |
|---|---|---|
| Definitions; Board’s constitution and procedure | In force | 13 Nov 2025 |
| Penalty schedule; power to make rules and remove difficulties | In force | 13 Nov 2025 |
| RTI Act amendment (s.44(3)) | In force | 13 Nov 2025 |
| Board Chairperson and four Members | Not appointed (recruitment advertised 6 Jun 2026) | Pending |
| Consent Manager registration (Rule 4) | Scheduled | 13 Nov 2026 |
| Notice, consent, legitimate uses, security safeguards | Scheduled | 13 May 2027 |
| Children’s data, breach reporting, individuals’ rights | Scheduled | 13 May 2027 |
| Complaints to the Board and penalties actually imposed | Scheduled | 13 May 2027 |
| IT Act Section 43A and SPDI Rules | Still apply until replaced | Omitted 13 May 2027 |
What the DPDP Act Means for an Ordinary Internet User
Once the main phase is in force. Subject to the Act’s exemptions and the Rules.
| Concept | What it means in practice |
|---|---|
| Notice | Before or when asking for consent, the Data Fiduciary must say what data it collects, why, and how you can exercise your rights and complain. |
| Consent | Must be free, specific, informed, unconditional and unambiguous, by a clear affirmative action, and limited to data needed for the purpose. It can be withdrawn as easily as it was given. |
| Legitimate uses | Section 7 allows processing without consent in listed cases, such as data you volunteered for a purpose, state benefits, legal duties, medical emergencies and employment. |
| Security safeguards | Reasonable security measures to prevent breaches, including encryption or masking, access controls and logs, under Rule 6. |
| Rights | Access to a summary of your data, correction and erasure, grievance redressal, and nomination. |
| Children’s data | Verifiable parental consent; no tracking, behavioural monitoring or targeted ads at children. |
| Accountability | Data Protection Board inquiries and penalties up to ₹250 crore per breach. |
Would you trade privacy for convenience?
A fictional free app offers personalised recommendations and asks for your contacts, location, photos, microphone and payment history. Choose how much to share to see the trade-off. This is an explainer, not legal advice; no answers are recorded.
Choose an option above
The Penalty Schedule
Maximum amounts per instance under the Schedule to the Act. The Board decides the actual amount, considering factors such as the nature, gravity and duration of the breach.
| Breach | Maximum penalty |
|---|---|
| Failure to take reasonable security safeguards to prevent a breach | ₹250 crore |
| Failure to notify the Board and affected people of a breach | ₹200 crore |
| Breach of additional obligations on children’s data | ₹200 crore |
| Breach of Significant Data Fiduciary obligations | ₹150 crore |
| Breach of a voluntary undertaking accepted by the Board | Up to the penalty for the original breach |
| Any other breach of the Act or Rules | ₹50 crore |
| Breach of a Data Principal’s own duties | ₹10,000 |
Twenty-Seven Years, Three Eras
How India went from a cyber law to a privacy law.
The cyber-law era (2000–2011). The Information Technology Act of 2000 was written for e-commerce and cybercrime. Personal data entered the law only with the 2008 amendments, which took effect in October 2009: Section 43A made companies pay compensation if they negligently failed to protect “sensitive personal data”, and Section 72A punished disclosure of personal information in breach of a contract. The 2011 SPDI Rules defined that sensitive data and required privacy policies and consent. The regime was narrow: it covered only body corporates, only sensitive data, and offered compensation through a slow adjudication process.
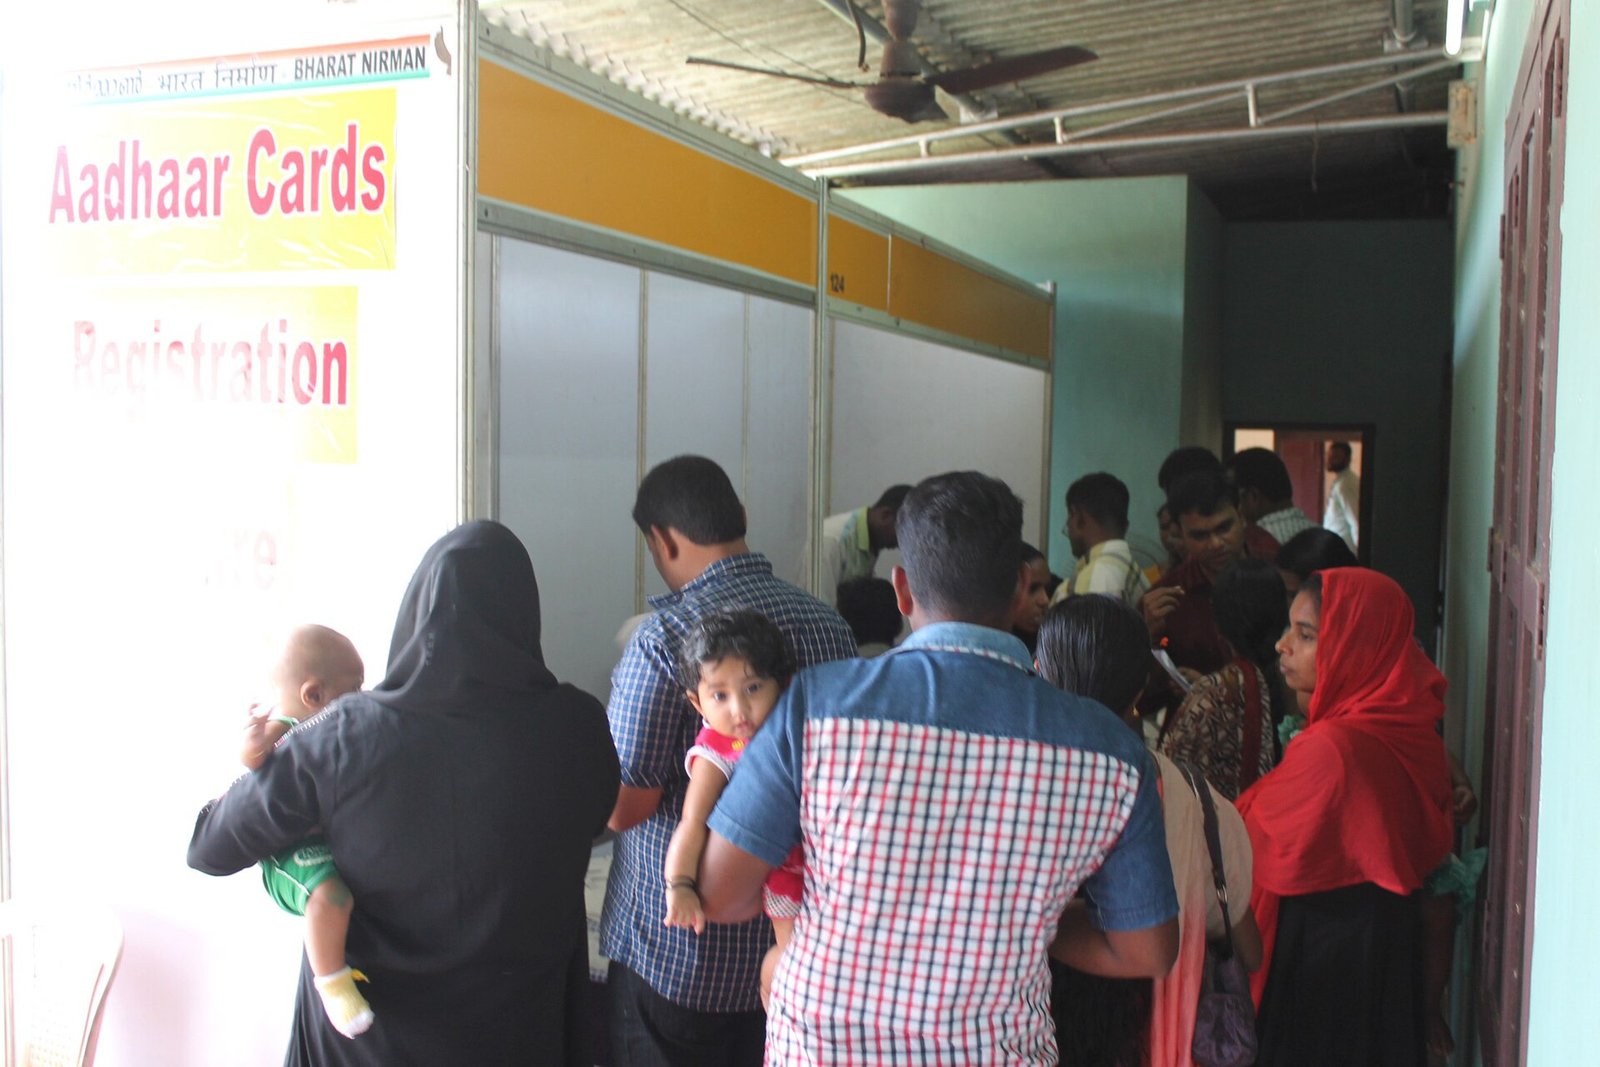
The rights era (2012–2018). The push for a real law came from Aadhaar. In 2012 retired judge K.S. Puttaswamy challenged the biometric ID scheme, the same year the A.P. Shah expert group proposed national privacy principles. When the government argued that Indians had no fundamental right to privacy, the question went to a nine-judge bench. On 24 August 2017 it ruled unanimously that they do, and that informational privacy is part of that right. Weeks earlier, on 31 July 2017, the government had set up the Srikrishna Committee, whose 2018 report and draft bill shaped everything that followed.
The legislative era (2019–2027). The 2019 bill gave the government wide exemptions, which Justice Srikrishna himself criticised, and was withdrawn in 2022 after a two-year committee process. Its 2023 successor passed within a week. It is simpler and more business-friendly, with no sensitive-data category and no default localisation, but it keeps broad state exemptions and creates a Board rather than an independent regulator.
The 2019 Bill vs the 2023 Act
| PDP Bill, 2019 | DPDP Act, 2023 | |
|---|---|---|
| Scope | Digital and some offline personal data; JPC wanted non-personal data too | Digital personal data only (and offline data later digitised) |
| Sensitive data | Separate category with stricter rules | No separate category |
| Data leaving India | Sensitive data copy in India; “critical” data only in India | Allowed unless the government blacklists a country |
| Regulator | Data Protection Authority with rule-making powers | Data Protection Board: adjudicates and penalises |
| Penalties | Up to 4% of global turnover; some criminal offences | Fixed caps up to ₹250 crore; civil only |
| Government exemptions | Section 35, broad | Section 17, broad |
India’s Data Protection Law: The Full Timeline, 2000–2027
Newest first. Tags show what is in force, what is only scheduled, and what was dropped.
2027
The main phase is due Scheduled
The bulk of the framework is scheduled to apply: the Act’s application, grounds for processing, notice and consent, legitimate uses, the general obligations of Data Fiduciaries, children’s data, breach reporting, individuals’ rights and duties, Significant Data Fiduciaries, cross-border transfers, and the Board’s complaints and penalty powers. Section 43A of the IT Act is omitted on the same date.
2026
Consent Managers switch on Scheduled
The registration framework for Consent Managers begins: Indian companies that let people give, review and withdraw consent across many services through one interoperable platform. They must register with the Data Protection Board, which, as of the latest official answer, still had no members appointed.
2026
First “removal of difficulties” order 2026
MeitY issues the Digital Personal Data Protection (Removal of Difficulties) Order, 2026, which the government describes as textual corrections. It clarifies that verifiable consent in Section 9(1) covers personal data of a child or of a person with a disability, and that a Significant Data Fiduciary’s periodic audit in Section 10 is a data audit.
2026
Parliament asks: where is the Board? 2026 Unresolved
Asked why the Board set up in November 2025 still had no Chairperson or four Members, and whether any Consent Managers or breach complaints had been registered, the government replies that the recruitment advertisement was published in the Employment News on 6 June 2026 and that appointments go through a search-cum-selection committee. It gives no date for appointments.
2026
Board recruitment opens 2026
Six months after the Board legally came into existence, MeitY invites applications for its Chairperson and four Members. A LiveLaw analysis on 1 August notes that courts have already begun pointing petitioners to a Board that has no one to hear them.
2026
Safer Internet Day: “Smart Tech, Safe Choices” 2026
India’s campaign focuses on the safe and responsible use of AI, with a newsletter on AI-enabled frauds, cyber-hygiene sessions and outreach through public media. MeitY reports an estimated 9.78 crore people reached and 3.95 crore additional digital impressions. Awareness campaigns and data law work side by side: the law sets duties for organisations, awareness teaches people to protect themselves.
2025
DPDP Rules notified; phase one in force In force
MeitY notifies the Digital Personal Data Protection Rules, 2025 together with a commencement notification that switches the framework on in three phases over 18 months. Phase one covers definitions, the constitution and procedures of the Data Protection Board (four members plus a Chairperson, functioning digitally), penalties, powers to make rules and remove difficulties, and the amendment of the RTI Act’s personal-information exemption.
2025
Draft Rules out for consultation History
The draft Rules set out notice formats, Consent Manager conditions, breach reporting, children’s consent verification, data retention for large platforms and the Board’s procedures. MeitY extends the comment deadline after requests from industry. PIB later reports 6,915 inputs; MeitY’s own summary of submissions puts the figure at 6,951.
2023
The DPDP Act becomes law History
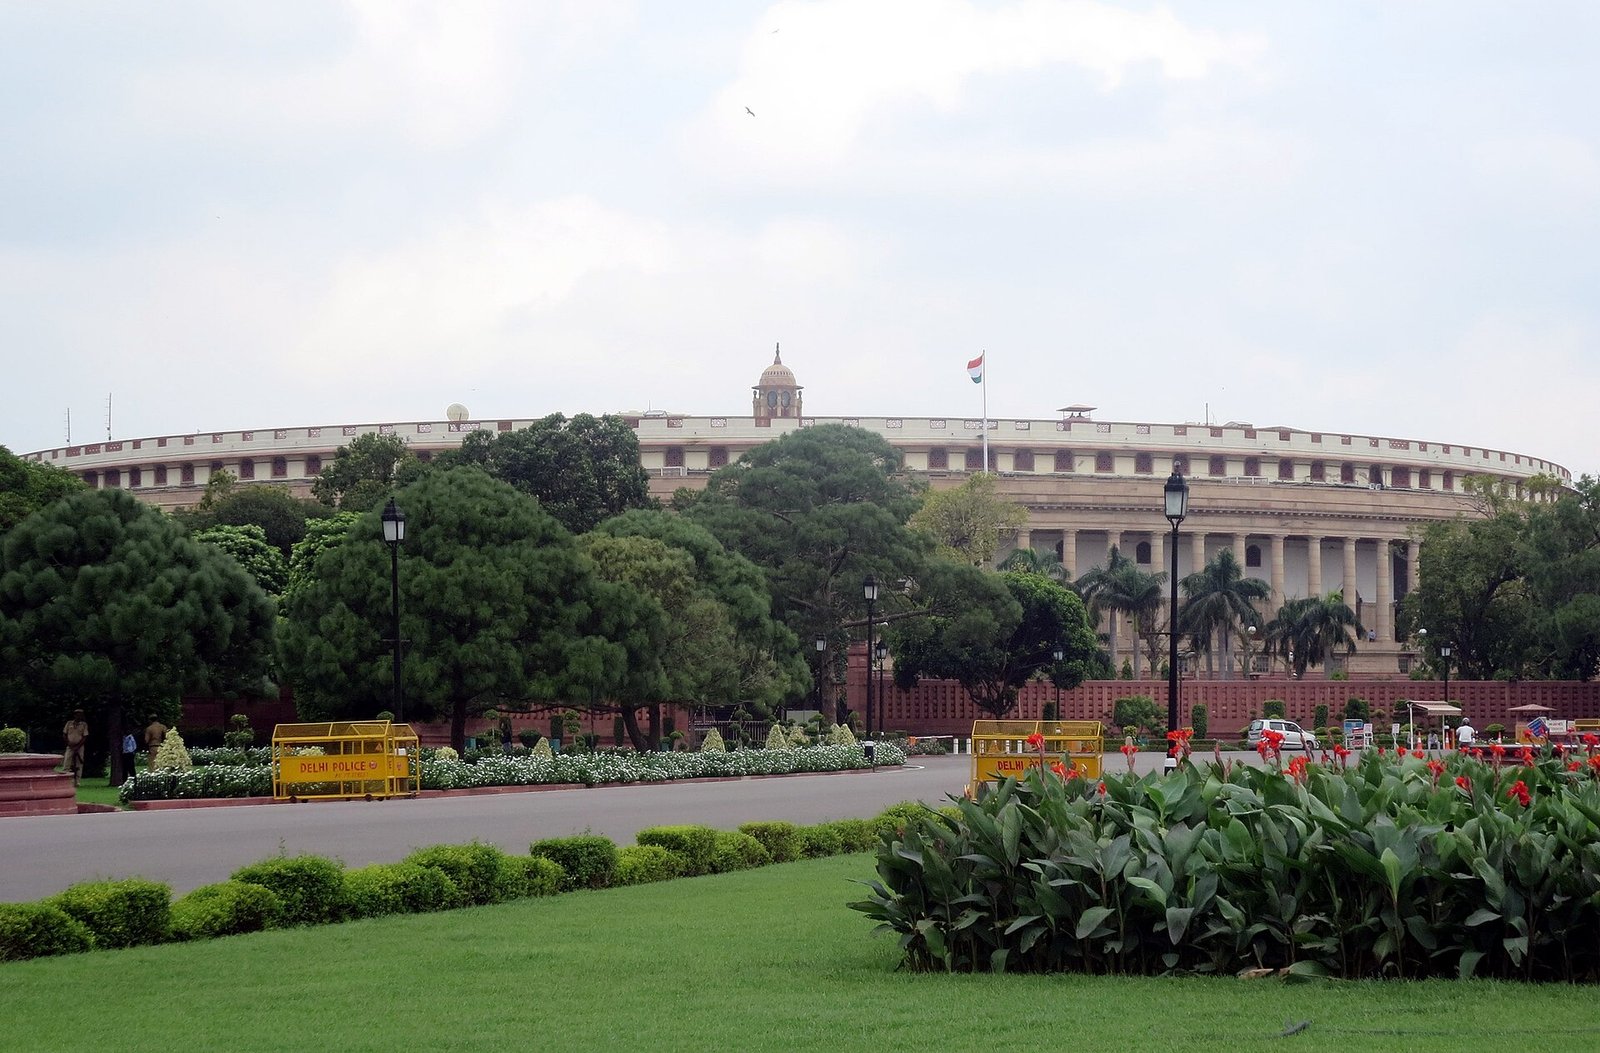
The Digital Personal Data Protection Bill passes both Houses within a week of introduction and receives presidential assent. It is far shorter than the 2019 bill and sets up a Data Protection Board rather than a regulator. Assent does not make it operative: the government must notify commencement, which takes two more years.
2022
A new draft: the DPDP Bill, 2022 History
MeitY publishes a much slimmer draft built only around digital personal data. It notably uses “her” and “she” for all individuals, drops mandatory localisation, and proposes penalties of up to ₹500 crore per instance. The bill introduced in 2023 lowers the cap to ₹250 crore.
2022
The 2019 bill is withdrawn Dropped
After the Joint Parliamentary Committee’s report in December 2021 recommended 81 amendments and widened the bill to cover non-personal data, the government withdraws it, promising a “comprehensive legal framework”. Supporters of a strong law call it a lost two years; industry welcomes a fresh start.
2019
Personal Data Protection Bill, 2019 History
Based on the Srikrishna draft but with wider government exemptions, the bill proposes a Data Protection Authority, a sensitive-personal-data category and local storage of “critical” data. Justice Srikrishna himself warns it could turn India into an “Orwellian state”.
2018
The Aadhaar judgment History
Applying the privacy right, the Supreme Court upholds the Aadhaar scheme for welfare and tax but strikes down Section 57, which had let private companies demand Aadhaar for verification. Banks and telecom companies can no longer make it mandatory.
2018
The Srikrishna Committee reports History
The committee, set up on 31 July 2017, proposes consent-based processing, rights for individuals, a powerful independent Data Protection Authority and storing at least one copy of personal data in India. It frames the problem as protecting individuals while letting the digital economy grow.
2017
Privacy becomes a fundamental right History
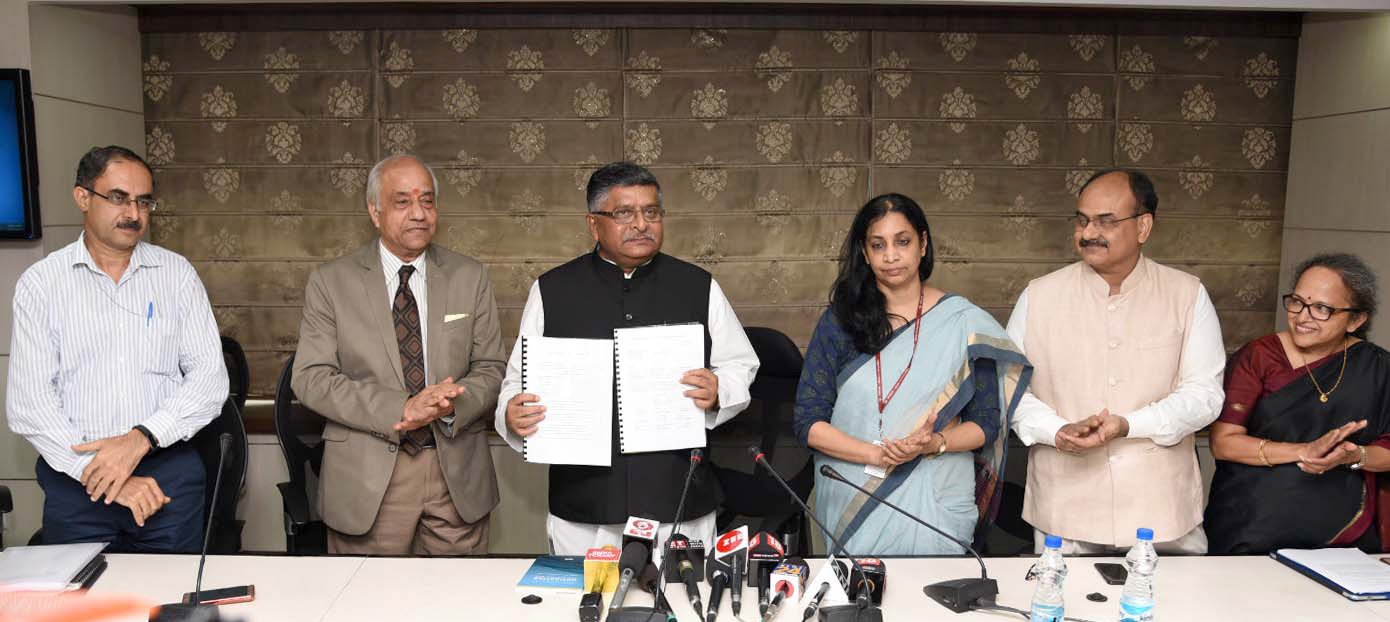
A nine-judge Constitution Bench unanimously holds that privacy is protected under Article 21 and Part III of the Constitution, overruling earlier cases (M.P. Sharma, 1954, and Kharak Singh, 1962). Informational privacy is recognised as part of it, and the court urges the government to enact a data protection law. The case began in 2012 as a challenge to Aadhaar.
2015
Section 66A struck down History
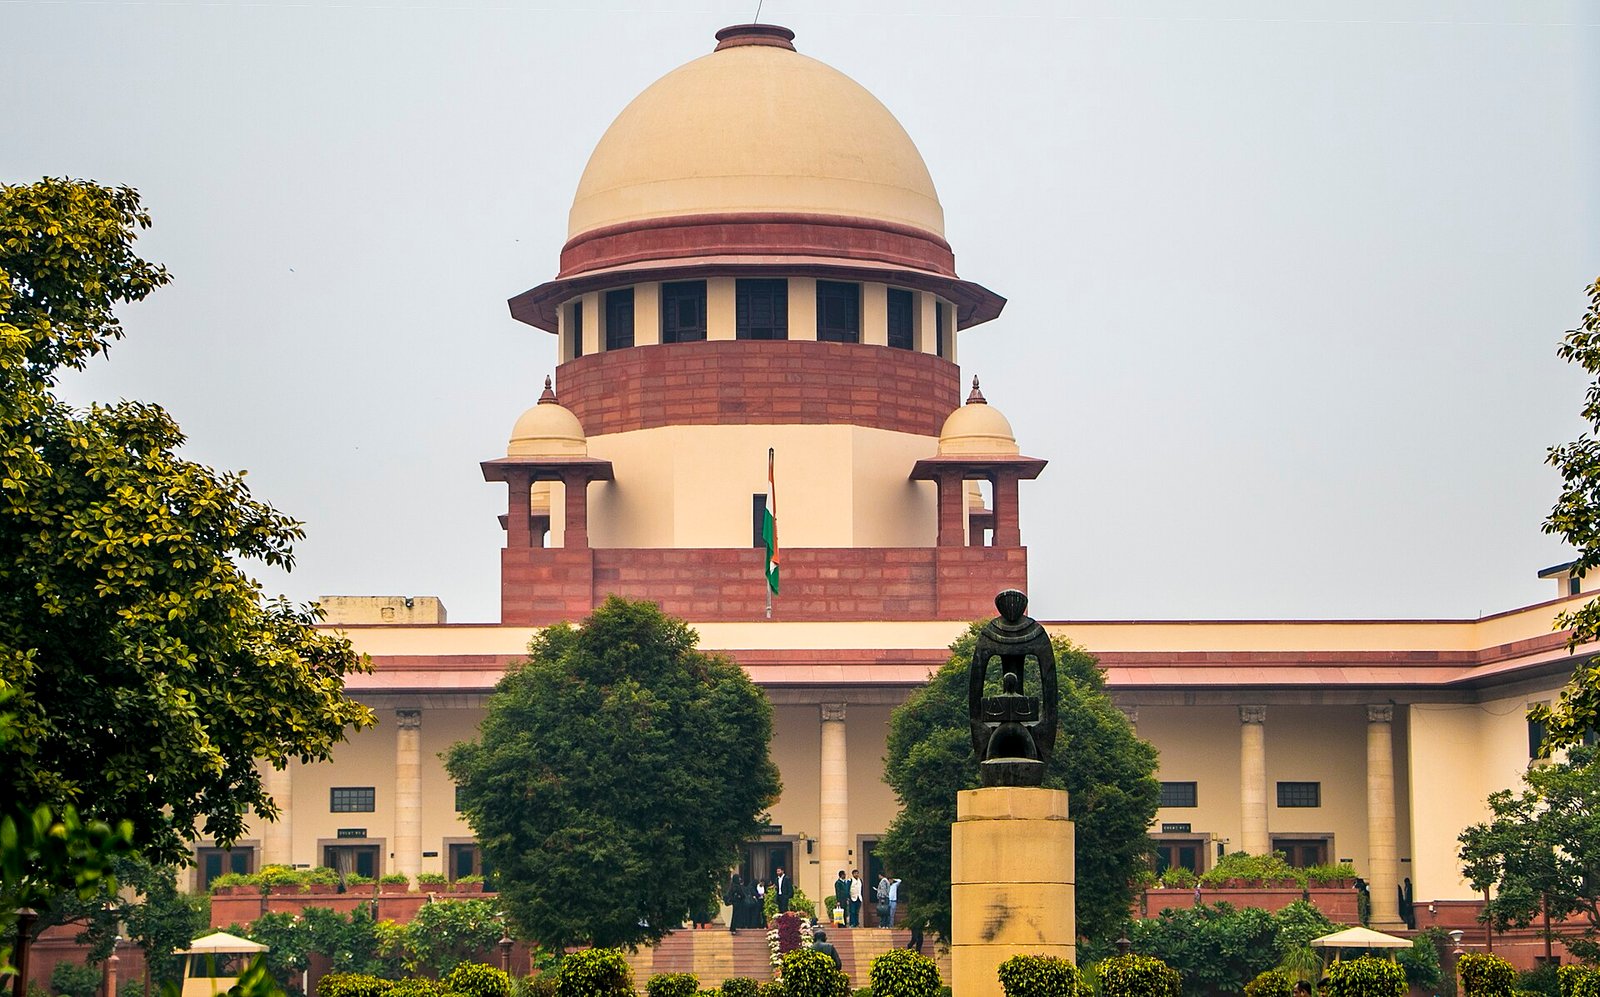
The Supreme Court strikes down Section 66A of the IT Act, which had made “offensive” online messages a crime and led to arrests over Facebook posts. It is a speech case, not a privacy case, but it shows the 2008 amendments needed constitutional pruning.
2012
The A.P. Shah expert group History
A group led by former Delhi High Court Chief Justice A.P. Shah proposes nine privacy principles, including notice, choice and consent, purpose limitation and accountability, and a privacy commissioner. Much of today’s vocabulary first appears here.
2011
The SPDI Rules History
Made under Section 43A, the Rules define sensitive personal data such as passwords, financial, health and biometric information, and require body corporates to publish privacy policies, take consent for collecting it and follow reasonable security practices such as ISO 27001. They do not bind the government.
2009
The IT (Amendment) Act, 2008 takes effect History
Passed in December 2008 without debate in the Lok Sabha, the amendment adds the first explicit data protection duties: compensation under Section 43A when a company negligently fails to protect sensitive data, and criminal liability under Section 72A for disclosing personal information in breach of contract. It also creates offences for identity theft, cheating by personation and violation of privacy through images.
2000
The Information Technology Act comes into force History
India’s first cyber law gives legal recognition to electronic records and digital signatures and creates offences such as hacking. It is a law for e-commerce and cybercrime, not for privacy, and says almost nothing about how organisations should handle personal data.
Corrections to Claims Circulating Online
From the summary material this page was built from, checked against the Gazette notifications, PIB, Lok Sabha answers and legal reporting.
“February 2025: the consultation period continues”
The deadline was 18 February 2025, then extended to 5 March 2025. PIB later cited 6,915 inputs; MeitY’s own summary says 6,951.
The Board has no members
Describing the Board as set up in November 2025 is true only in law. The government told the Lok Sabha on 12 August 2026 that recruitment was advertised on 6 June 2026.
The RTI amendment is already in force
Section 44(3), which changes the RTI Act’s personal-information exemption, came into force on 13 November 2025, not in 2027.
“2008: cyber-law amendments”
Passed in December 2008, assent on 5 February 2009, in force on 27 October 2009. The data provisions that matter are Sections 43A and 72A.
Aadhaar and the Shah report
The privacy case began as an Aadhaar challenge in 2012, and the 2012 A.P. Shah principles and the 2018 Aadhaar judgment are key steps the summary skipped.
October 2026 order
The first Removal of Difficulties Order, dated 5 October 2026, corrected the text of Sections 9 and 10. It changes wording, not the phased dates.
Four Tests for India’s Privacy Law
Can people use their rights?
Notices must be readable in English or any of the 22 scheduled languages. Whether people read them, and know they can complain, is another matter.
Can organisations map their data?
Most firms must know what they hold, why, and for how long, and build consent and deletion into products by May 2027.
Will the Board be ready?
A Board without members cannot register Consent Managers or hear complaints. Appointments before 13 November 2026 are the first test.
Will the state hold itself to the law?
Broad Section 17 exemptions mean the biggest data holder, the government, can exempt its own agencies. Critics see this as the law’s main gap.
What Remains Contested
- Government exemptions: privacy groups say Section 17 lets agencies escape the law on vague grounds; the government says national security requires it.
- The RTI change: transparency campaigners say it shields officials’ conduct from disclosure; the government says it protects personal privacy.
- Board independence: members are chosen through a government-led process and the Board sits under MeitY’s framework, unlike regulators with statutory independence.
- Children’s consent: treating everyone under 18 as a child needing parental consent is criticised as impractical for teenagers and a push towards age verification.
- Timeline: industry has sought more time; privacy advocates say 18 months on top of two years was already long.
How to Stay Safer Online Now
General habits, not legal advice. They work whether or not a particular provision is in force.
- Check app permissions: does a torch or game really need contacts, microphone or location?
- Use unique passwords and two-factor authentication: a password manager makes this practical.
- Verify before you pay: confirm payment requests and links through a channel you trust; never share OTPs.
- Share less: avoid posting Aadhaar, PAN, bank details or documents; use masked Aadhaar where accepted.
- Review privacy settings: check who sees your posts, profile and location.
- Be careful with AI tools: do not paste passwords, confidential work files or financial details into chatbots.
- Know where to report: cybercrime.gov.in or 1930 for fraud; the company’s grievance officer for data complaints.
What to Watch
- Board appointments: whether the Chairperson and Members are named before Consent Managers start.
- 13 November 2026: the first Consent Manager registrations.
- Significant Data Fiduciaries: which companies the government designates.
- Further orders or amendments: any change to the 13 May 2027 date.
- 13 May 2027: the main phase, and the first complaints the Board hears.
Quick Quiz
1. When did the DPDP Act receive presidential assent?
2. Which case declared privacy a fundamental right?
3. What starts on 13 November 2026?
4. What is the largest penalty under the DPDP Act?
5. What was India’s Safer Internet Day 2026 theme about?
Explore More Timelines
People Also Ask
Frequently Asked Questions
A Law on Paper, Privacy in Practice
India’s data protection story runs from a cyber law written before smartphones, through a constitutional judgment and two abandoned bills, to a law that is still switching on. Safer Internet Day is a reminder that legal duties and personal habits are different tools: the law tells organisations what they owe you, and awareness helps you notice when they fall short.
The real measure of the DPDP Act will not be the number of pages in it, but whether, after May 2027, an ordinary user can find out what an app knows about them, get it deleted, and have a complaint heard by a Board that actually sits.
Related AiTimeline Stories
⚠️ Editorial Note
Last updated 9 October 2026. This page is general information, not legal advice. Commencement dates are calculated from the Gazette date of 13 November 2025 and reflect the official notifications and the government’s Lok Sabha answer of 12 August 2026; check the latest Gazette notifications and any amendments before relying on a date for compliance. Criticism of the Act is attributed to those who make it. Sources are listed below.
Sources & further reading
Every dated entry above was checked against these references. Last reviewed 9 October 2026.
- Wikipedia: Digital Personal Data Protection Act, 2023
- MeitY: Data protection framework (DPDP Act and DPDP Rules, 2025)
- PIB: Explanatory note on the Digital Personal Data Protection Rules, 2025 (Nov 2025)
- Lok Sabha Unstarred Question 3960: Appointment of Chairperson and Members of the Data Protection Board (12 Aug 2026)
- LiveLaw: India's Data Protection Board, established in law, absent in fact (1 Aug 2026)
- India Briefing: DPDP Removal of Difficulties Order 2026 (7 Oct 2026)
- C-DAC / ISEA: Safer Internet Day 2026
- India Code: The Information Technology (Amendment) Act, 2008